Autonomous Enterprise Velocity: Expanding Across the GCC Without Multiplying Complexity

Insights / Autonomous Enterprise Velocity: Expanding Across the GCC Without Multiplying Complexity
GCC Expansion Architecture for CEO

Enterprises that have built genuine Autonomous Enterprise Velocity in the UAE often make the same assumption when they look at the rest of the Gulf: that expanding from Dubai or Abu Dhabi into Riyadh, Doha, or Manama is largely a translation and localisation exercise. Same region, similar culture, comparable customer expectations. The technology stack that works in the UAE should simply extend outward.

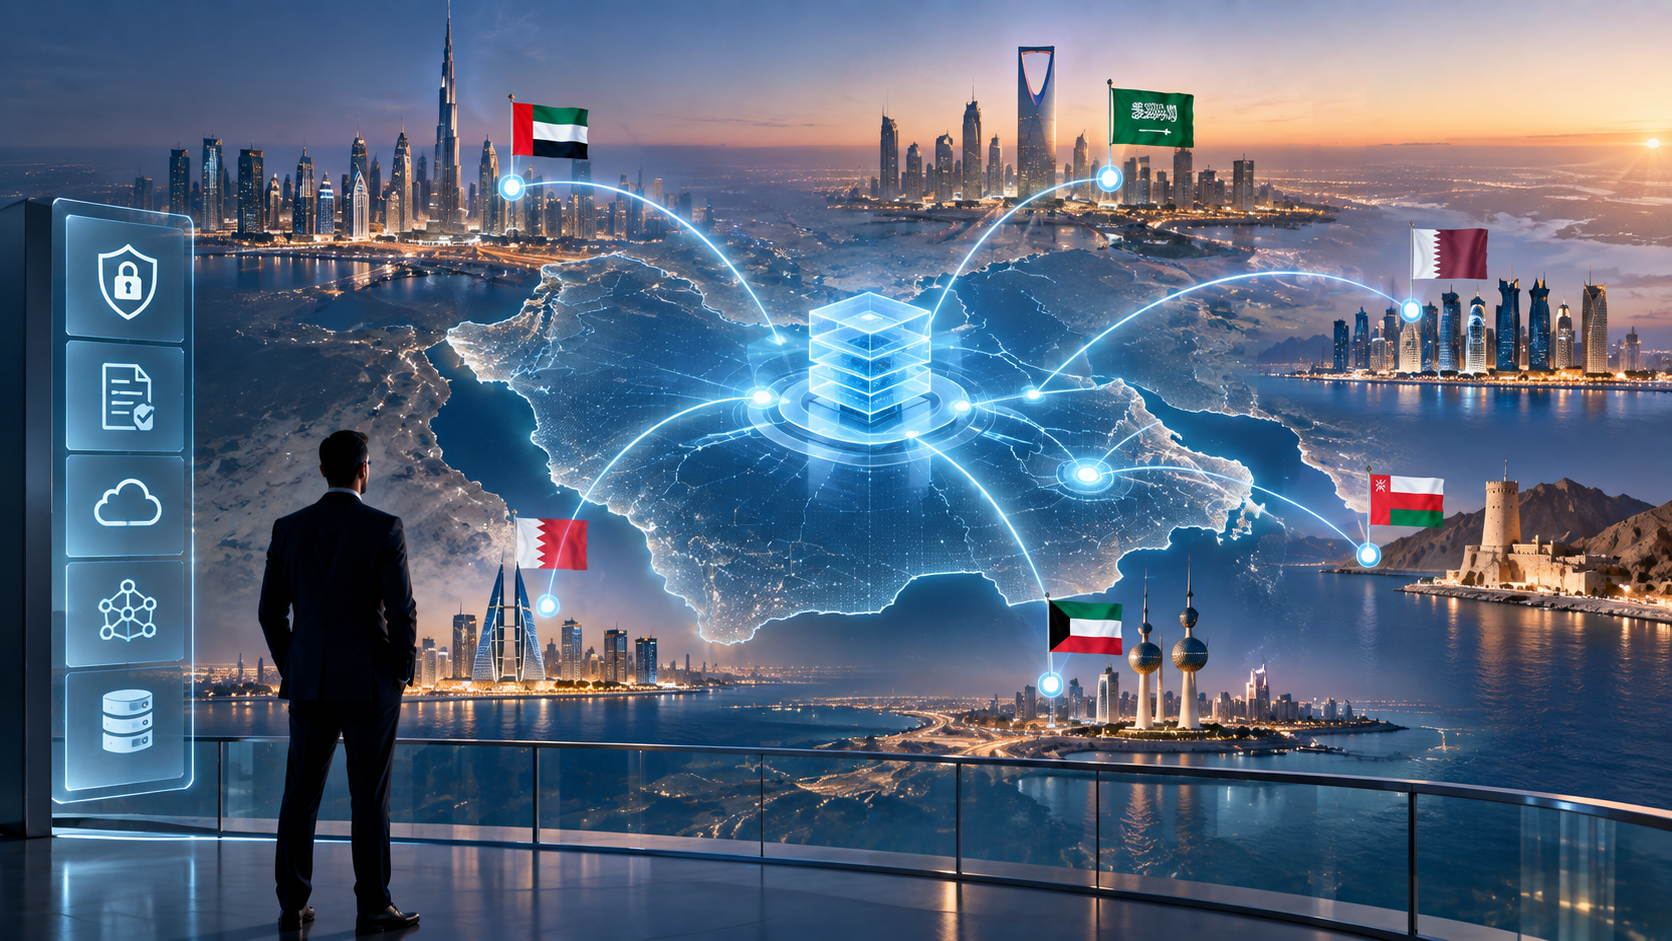
That assumption is wrong in a way that has real cost attached to it. The GCC is not one regulatory market wearing six flags. It is six separate, substantively different data protection regimes, each with its own regulator, its own default position on cross-border data transfer, and its own approach to how AI systems that process customer data are expected to behave.

Six Countries, Six Regimes

A CEO planning GCC expansion needs to start from this table, not from a market-entry deck:

CountryRegulatorApproach
UAEUAE Data Office (+ DIFC, ADGM)Most GDPR-aligned; adequacy-based transfers
Saudi ArabiaSDAIAStrictest; localisation is the default position
QatarNCSAMore permissive by statute; sector and cloud policy add separate constraints
BahrainPDPAAdequacy list published; transfer restrictions where absent
OmanMTCITExecutive Regulations only fully in force since February 2026
KuwaitCITRASupervisory framework distinct from the other five

Where the Real Differences Actually Bite

The gap between the UAE and Saudi Arabia is the one that catches enterprises off guard. The UAE’s regime, anchored by the UAE Data Office alongside the DIFC and ADGM free-zone frameworks, is the most GDPR-aligned in the Gulf, built around adequacy-based transfer mechanisms that allow data to move where an equivalent standard of protection can be demonstrated.

Saudi Arabia’s PDPL, overseen by SDAIA, starts from a different default. Consent is the primary lawful basis rather than one option among several, the broader “legitimate interests” grounds enterprises rely on elsewhere are narrower, and data localisation is the default position rather than an exception that has to be justified. An architecture built around the UAE’s adequacy-based flexibility does not transfer cleanly into a market where the starting assumption runs the other way.

Qatar adds a different kind of trap. The NCSA’s statute is, on paper, comparatively permissive about cross-border transfer. But the real constraint on enterprises operating in Qatar often comes from sector-specific rules and government cloud policy rather than the privacy law itself — which means a compliance review that only reads the headline statute can miss the requirement that actually governs the workload.

Why “Is the Cloud Region in the GCC” Is the Wrong Question

This is the question most enterprise technology reviews default to, and it is the wrong one. The question that actually determines exposure is which legal and regulatory regime governs a given workload — a function of the type of data involved, which sector regulator has jurisdiction, what transfer mechanism is being relied on, and how the AI system itself processes and stores that data.

That last point matters more with every quarter of AI adoption. An AI system deployed across customer service, sales, and support does not just move customer data through a pipeline once. It generates continuous logs, inference records, and decision audit trails as a by-product of how it operates — and each of those artefacts is subject to the same jurisdiction-specific residency questions as the customer data that fed the system in the first place. A platform that is compliant on data-in but unexamined on data-generated-through-use is not actually compliant; it simply hasn’t been asked the harder question yet.

What Autonomous Enterprise Velocity Requires for GCC Expansion

Expanding across the Gulf without multiplying operational and compliance complexity requires treating the regulatory variation as an architecture decision made once, rather than a series of local patches applied market by market:

  • A per-country regulatory map built before the architecture decision, not after. Saudi Arabia, Qatar, Bahrain, Oman, and Kuwait each need their own answer to the residency and transfer questions, mapped before systems go live, not discovered during an audit.
  • Enterprise Data Sovereignty and Intelligence that respects each jurisdiction’s actual requirements. A single customer data architecture that can demonstrate compliance with the UAE’s adequacy-based model and Saudi Arabia’s localisation-first default at the same time, without maintaining two disconnected systems.
  • Clarity on which regulator’s rules actually apply. Especially in markets like Qatar, where the general privacy statute and sector-specific or cloud-policy rules diverge — the more restrictive requirement is the one that governs.
  • An architecture that can isolate data by jurisdiction while preserving one coordinated view for leadership. Regulatory separation at the data layer does not have to mean fragmented visibility at the leadership layer.
GCC Expansion Architecture CEO

Where Worktual's AI Advanced Intelligence Platform Fits

This is the kind of decision Worktual‘s AI Advanced Intelligence Platform is built to support: Enterprise Data Sovereignty and Intelligence architected around each jurisdiction’s actual regulatory requirements, rather than a single-market design stretched to cover six different regimes after the fact. For a CEO expanding out of the UAE, the platform decision gets made once — with Saudi Arabia’s localisation defaults, Qatar’s sector-specific constraints, and the other GCC markets’ requirements mapped in from the start, not retrofitted country by country as expansion accelerates.

Conclusion

GCC expansion rewards the enterprises that treat regulatory variation as an architecture question from day one, not the ones that treat the Gulf as a single market with minor local adjustments. The UAE’s more flexible, adequacy-based regime is not a template that transfers automatically to Saudi Arabia, Qatar, or the rest of the region — and the cost of discovering that during a compliance review is considerably higher than the cost of mapping it in advance.

Frequently Asked Questions

1. Do all GCC countries share the same data protection law?

No. The UAE, Saudi Arabia, Qatar, Bahrain, Oman, and Kuwait each operate their own data protection regime, with different regulators, different default positions on cross-border transfer, and different requirements for data localisation.

2. Why is Saudi Arabia’s data protection law considered the strictest in the GCC?

Saudi Arabia’s PDPL, regulated by SDAIA, treats consent as the primary lawful basis for processing rather than one option among several, narrows the legitimate-interests grounds enterprises often rely on elsewhere, and defaults to data localisation unless an exception applies.

3. Is the UAE’s data protection approach a good template for expanding into Saudi Arabia?

Not directly. The UAE’s regime is more GDPR-aligned and built around adequacy-based transfer mechanisms, which is a more flexible starting position than Saudi Arabia’s localisation-first default. An architecture designed only around the UAE’s flexibility will need real adjustment, not a light configuration change, to meet Saudi requirements.

4. Why does AI specifically raise the stakes on data residency in the GCC?

AI systems generate continuous logs, inference records, and decision audit trails as a by-product of normal operation. Those artefacts are subject to the same jurisdiction-specific residency questions as the customer data that feeds the system, which means compliance reviews that only examine data-in and miss data-generated-through-use are incomplete.

5. What should a CEO map before expanding operations across the GCC?

A per-country regulatory map covering each target market’s data protection regulator, its default position on cross-border transfer and localisation, and any sector-specific or cloud-policy rules that apply on top of the general privacy statute — built before the technology architecture is finalised, not after.

6. How does Worktual’s AI Advanced Intelligence Platform support GCC expansion?

It is built around Enterprise Data Sovereignty and Intelligence architected to each jurisdiction’s actual regulatory requirements, so the underlying platform decision is made once — with each GCC market’s residency and transfer requirements mapped in from the start rather than patched in market by market as expansion accelerates.